PublishedCVE-2026-8218·
3.4Low
A public exploit exists; no exploitation in the wild has been reported. EPSS puts the chance of exploitation in the next 30 days at 0%. No fixed version is recorded.
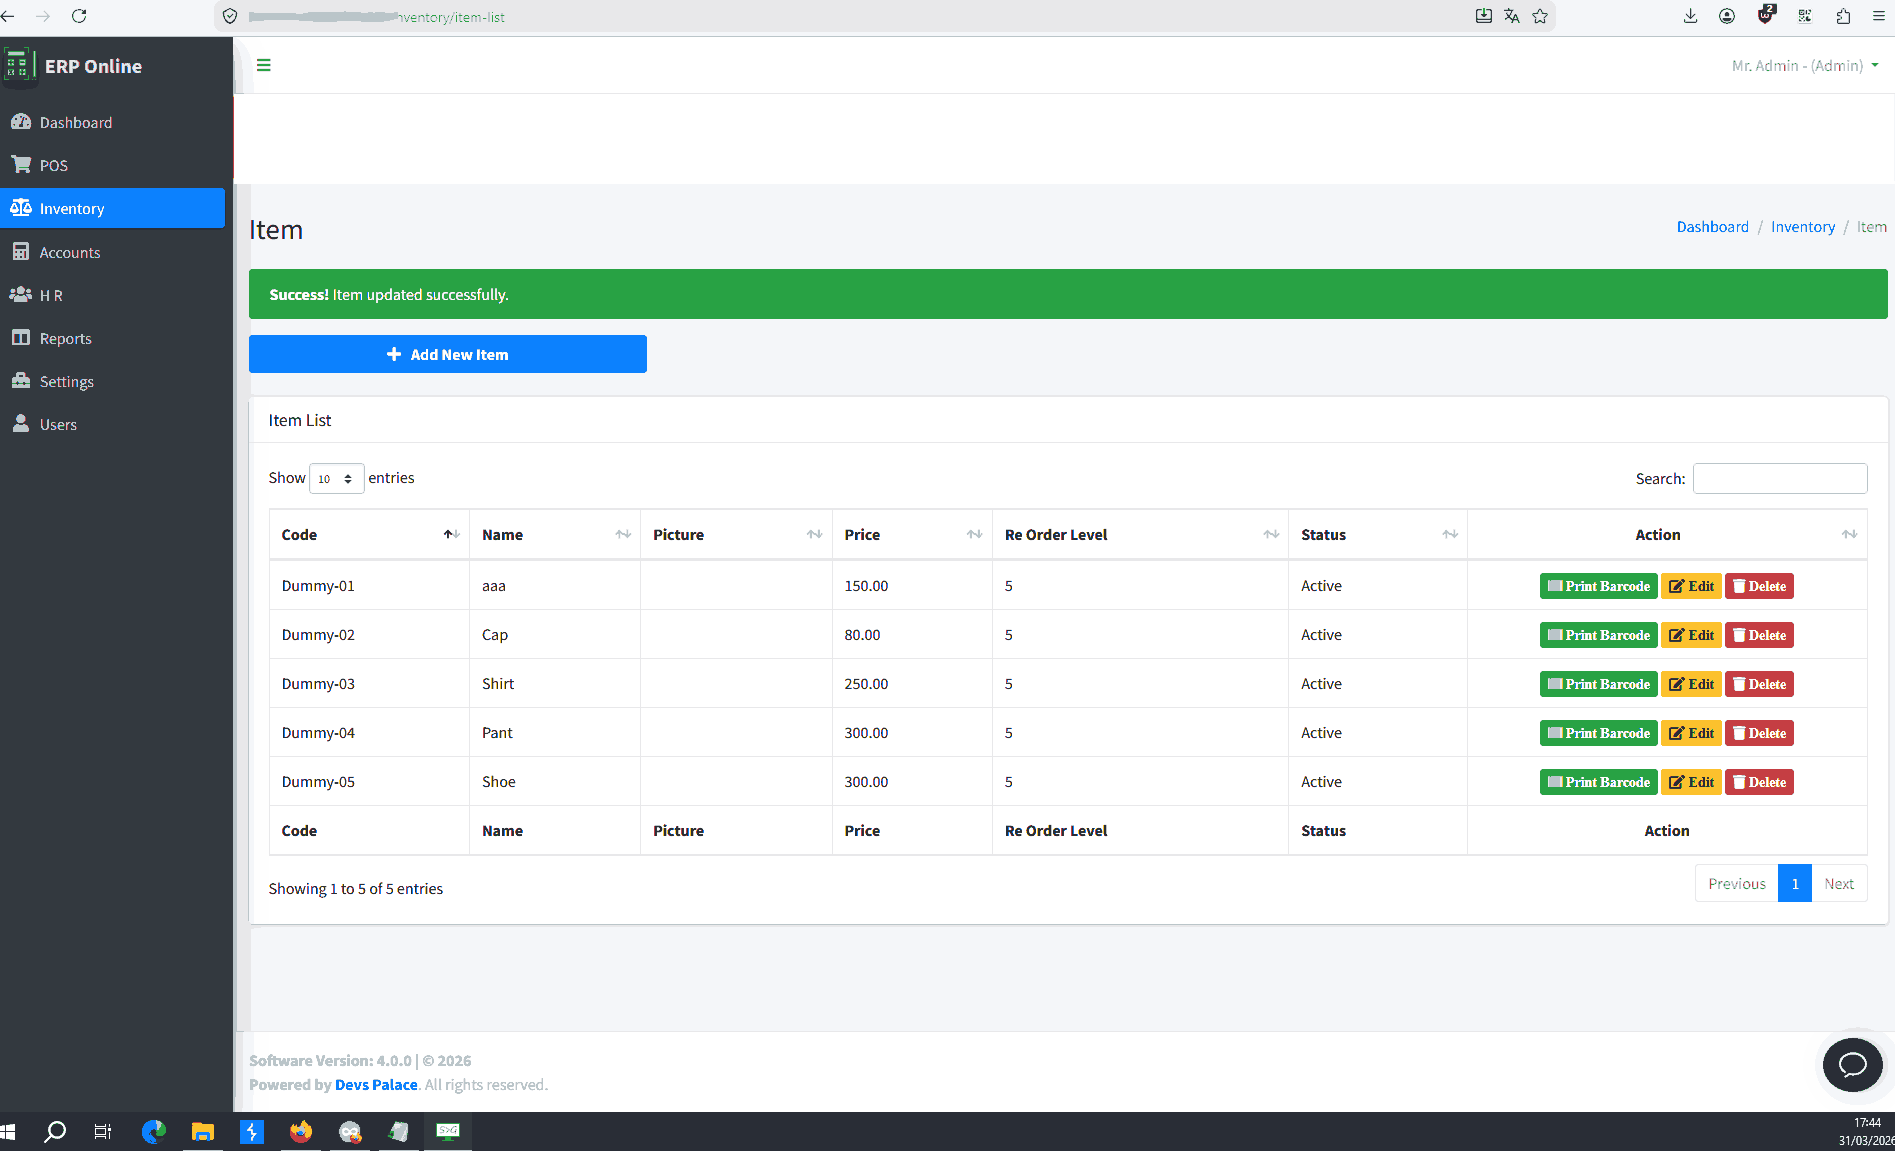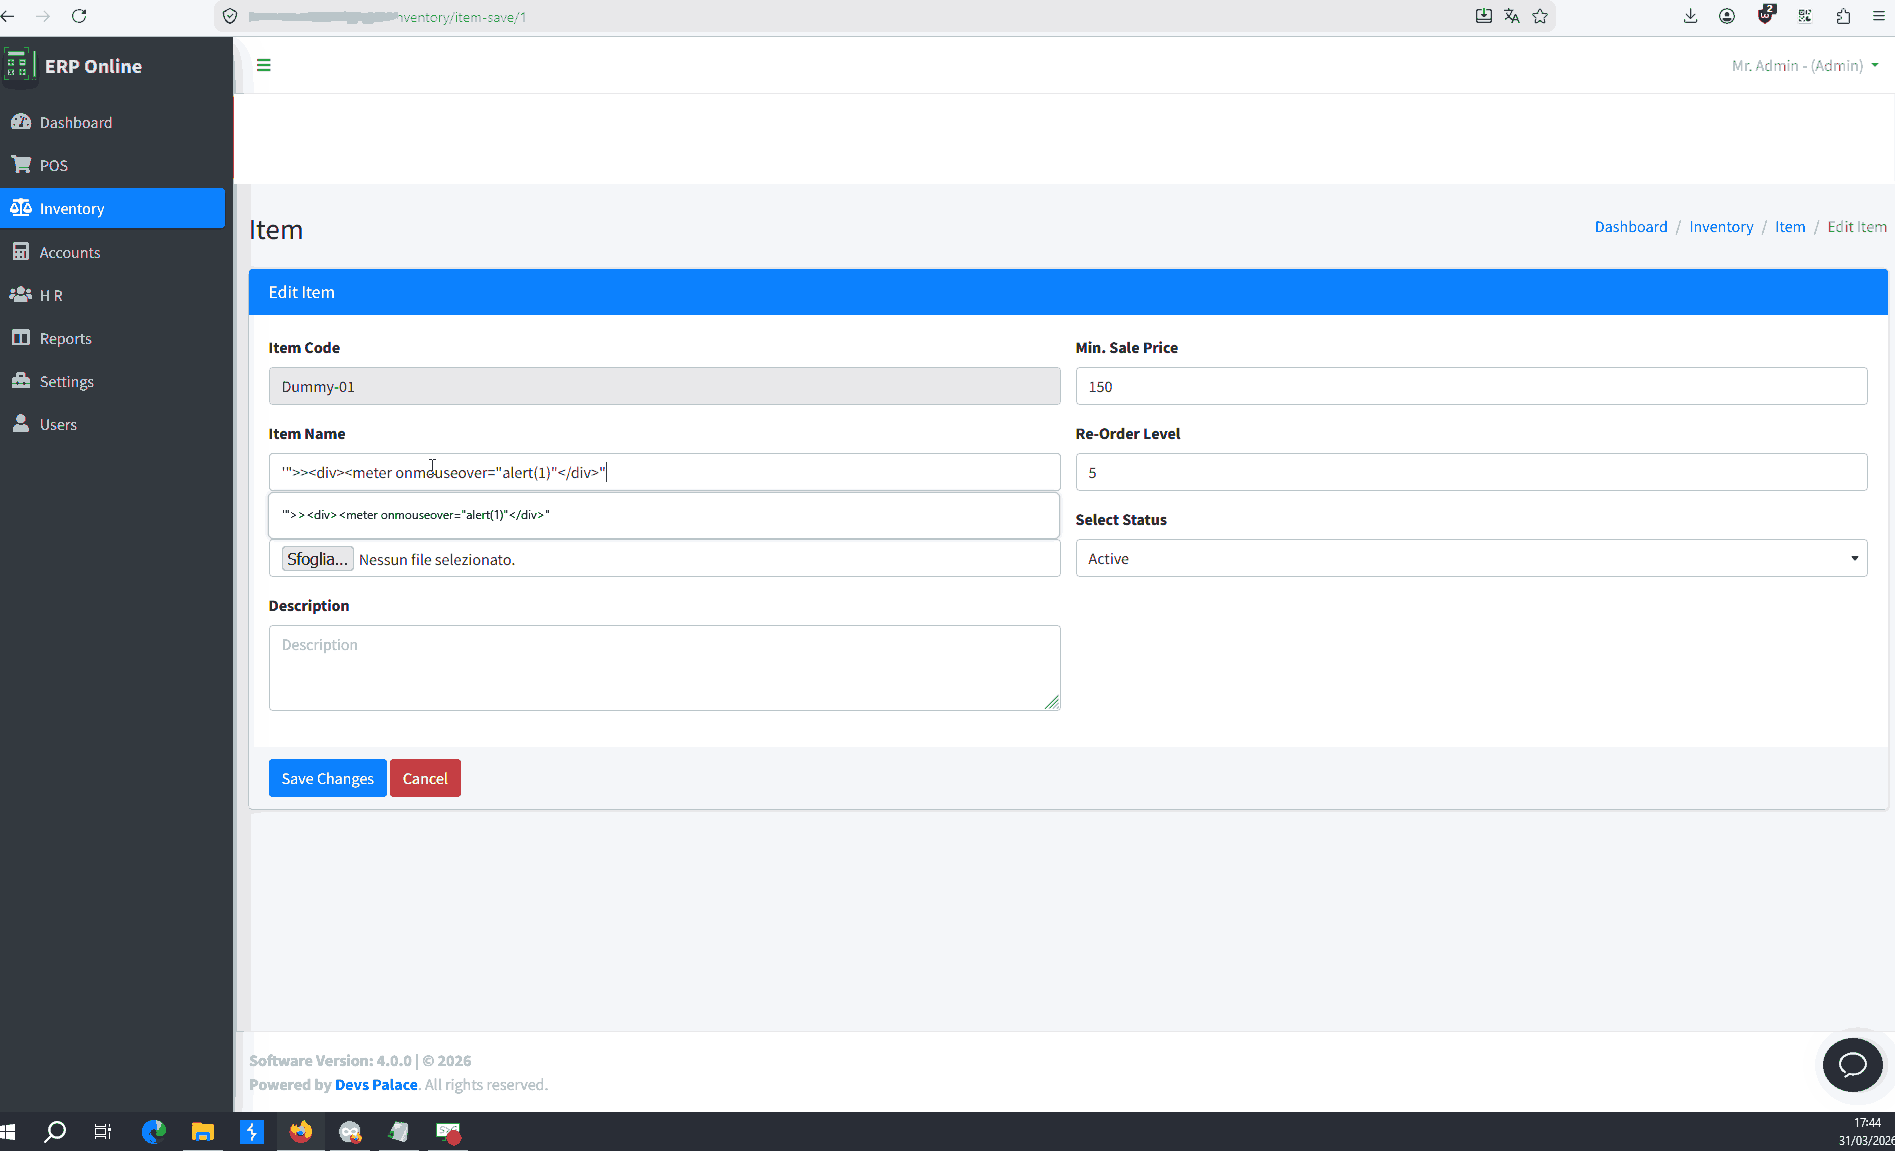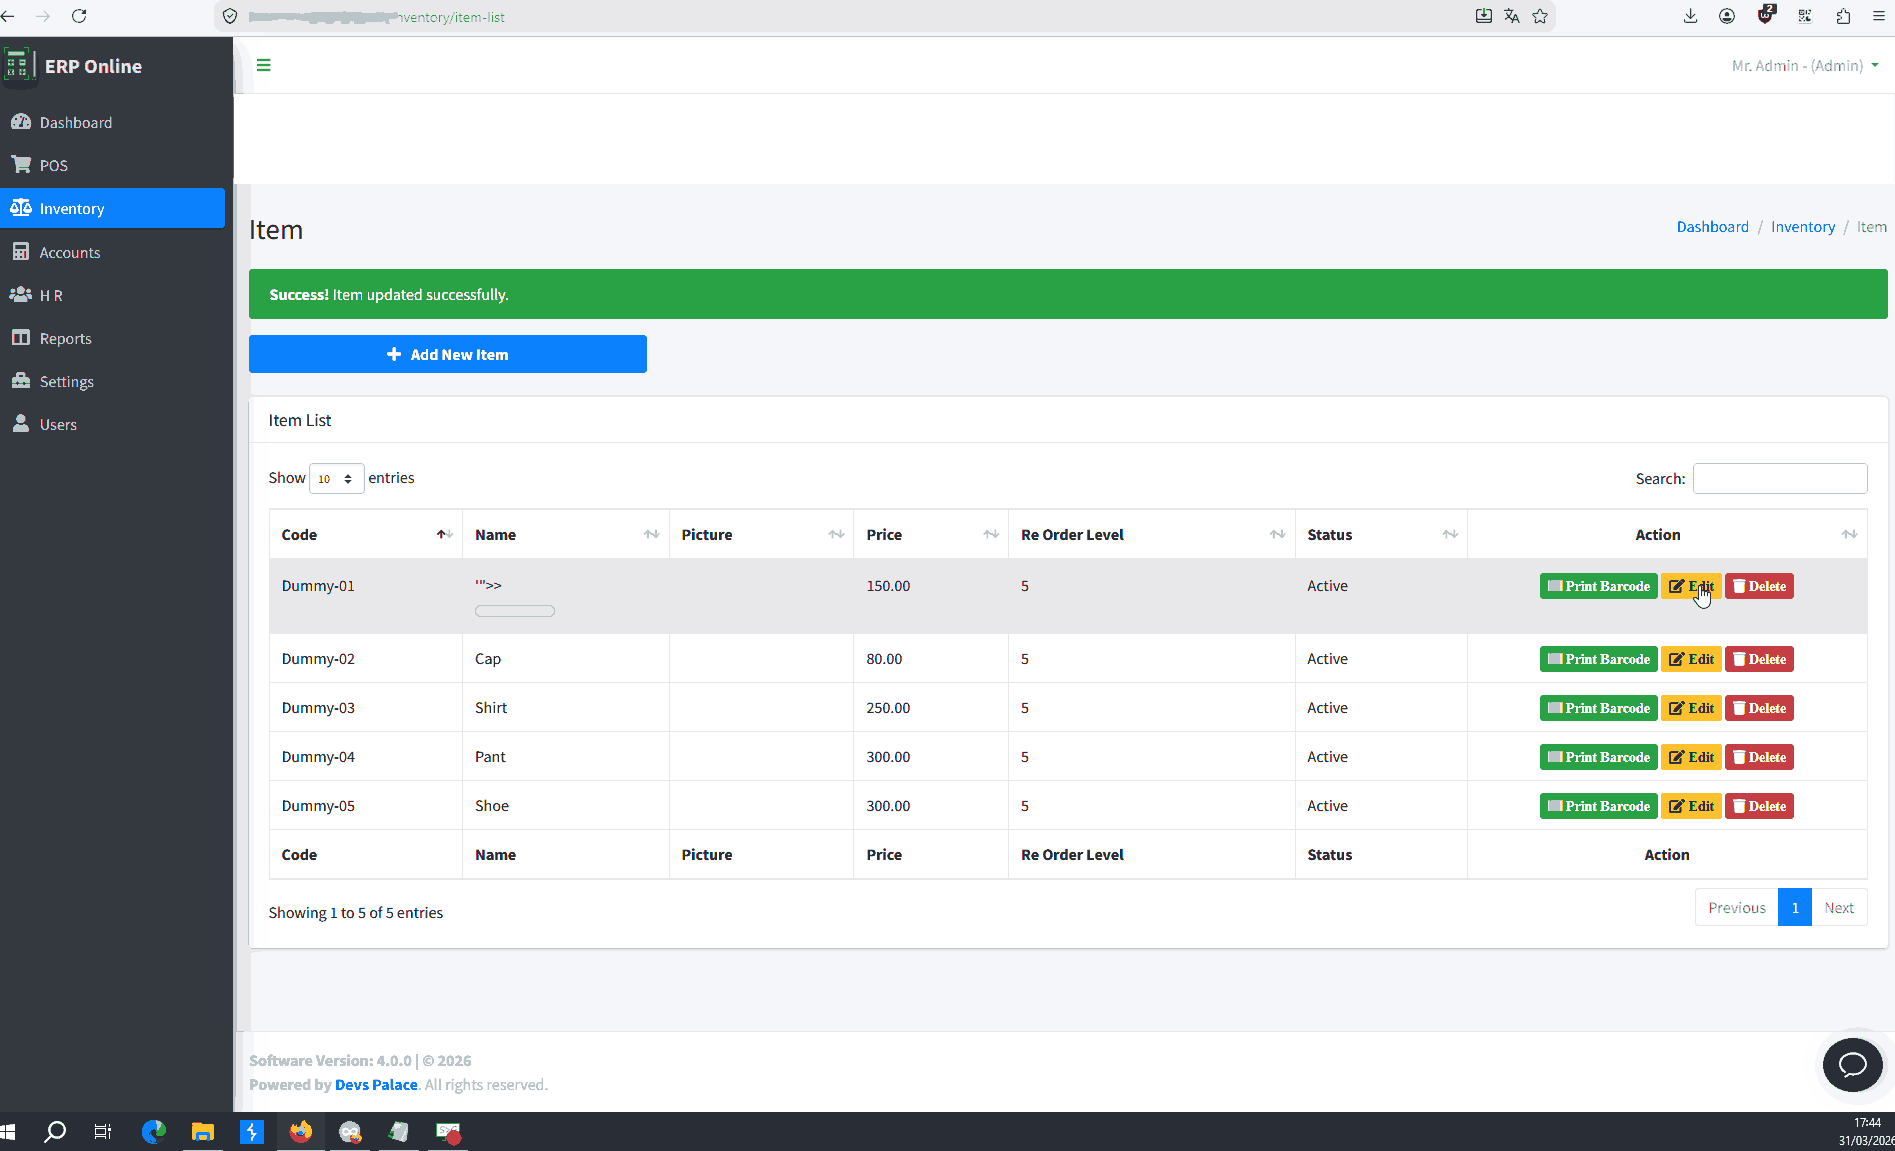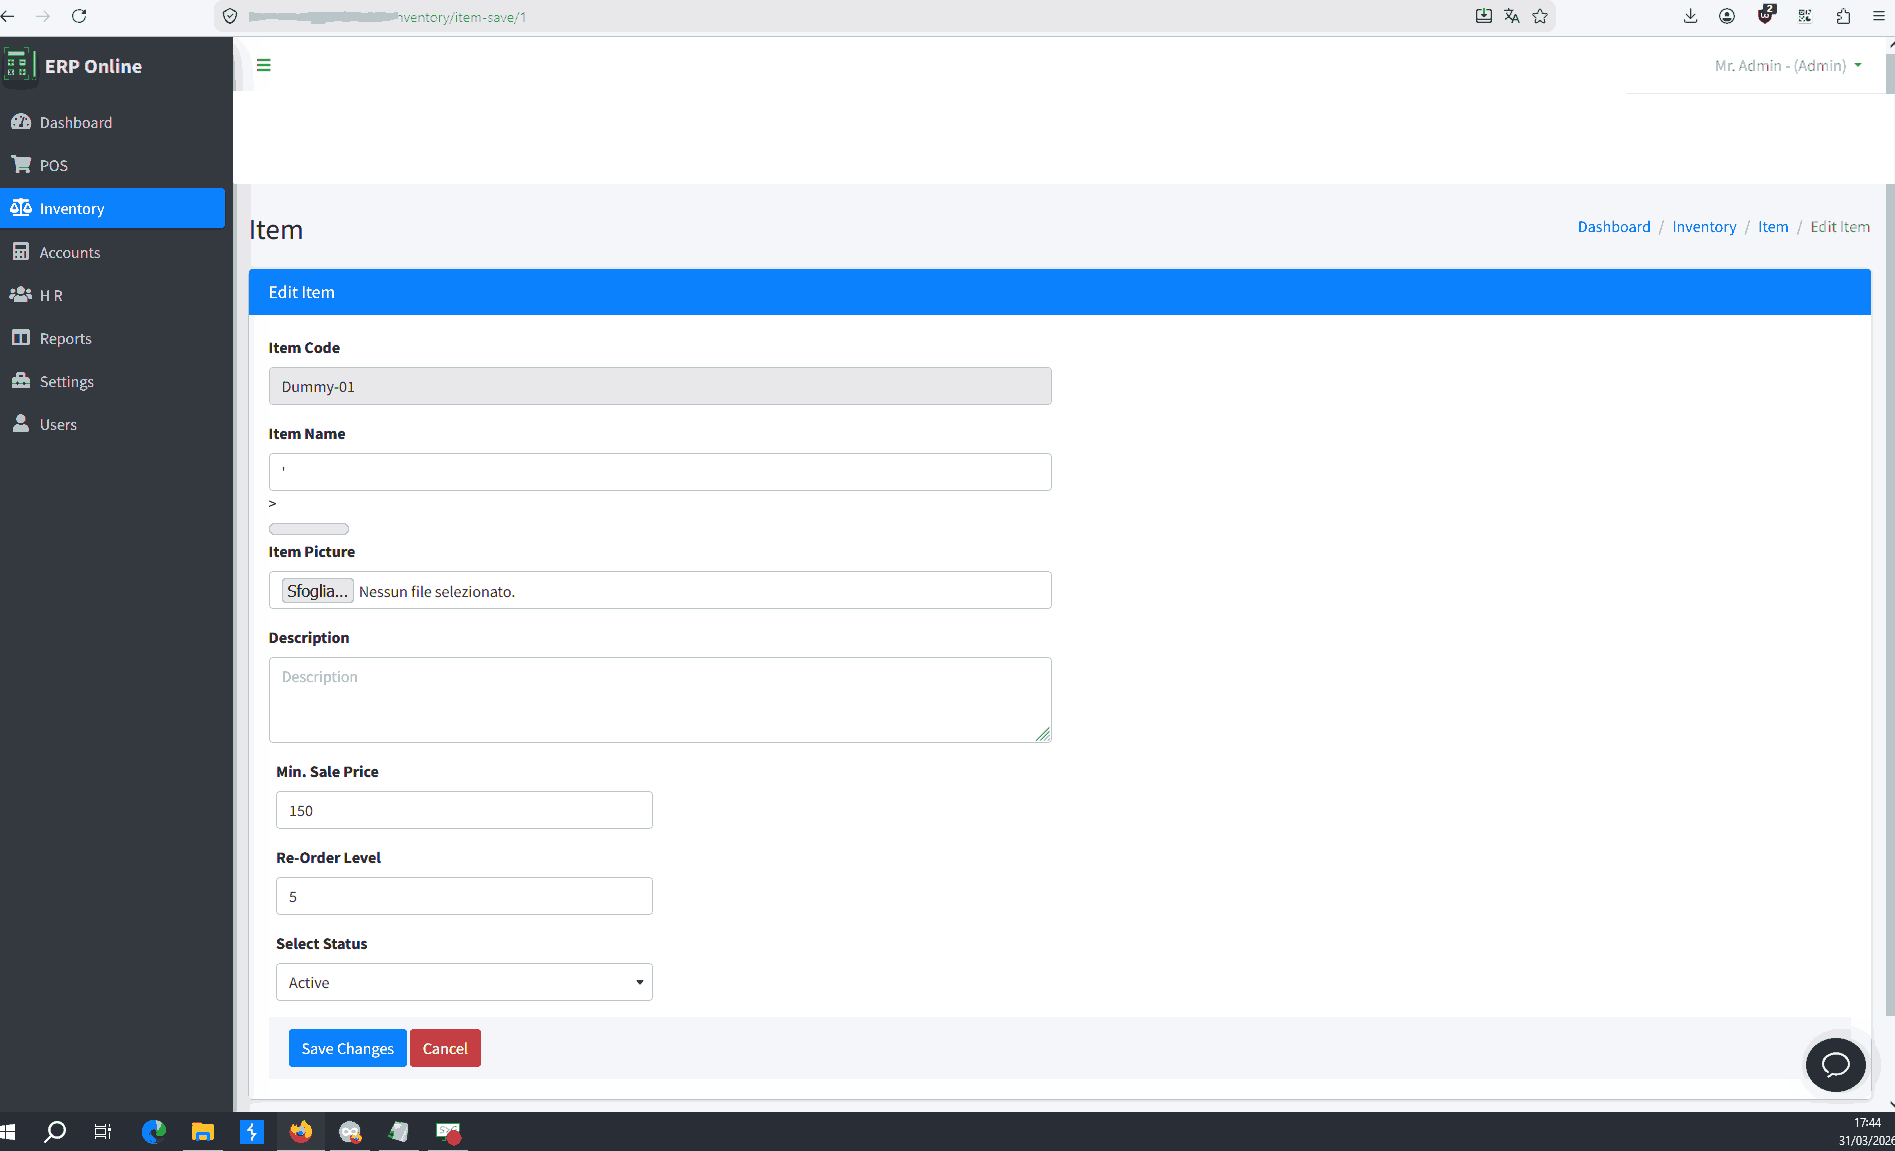
A weakness has been identified in Devs Palace ERP Online up to 4.0.0. The affected element is an unknown function of the file /inventory/purchase_return_save. Executing a manipulation can lead to cross site scripting. The attack may be launched remotely. The exploit has been made available to the public and could be used for attacks. The vendor was contacted early about this disclosure but did not respond in any way.
Vendors, products and packages with version ranges
| Vendor | Product | Versions | Fixed |
|---|---|---|---|
| Devs Palace | =4.0 |
1 public sources
Every event on this vulnerability
A live severity badge for an advisory, README or ticket
[](https://zeptric.io/cve/CVE-2026-8218)